Built by Mobeta, pentest experts for over 10 years
Pentest experts for over 10 years
A pentest does not end when the report is delivered.
A pentest does not end when the report is delivered.
No more forgotten PDF reports and manual retesting.
Centralize, recheck, and track your vulnerabilities continuously.
Centralize, recheck, and track your vulnerabilities continuously.
Book your 15-min demo
Book your 15-min demo
No commitment
·
Personalized by an expert
CYBERSECURITY
INNOVATION radar
The 2025 French
CYBERSECURITY
INNOVATION radarThe 2025 French
CYBERSECURITY
INNOVATION radarThe 2025 French
problem
The traditional pentest model has reached its limits
The traditional pentest model has reached its limits
Audit reports alone are no longer enough to guarantee your security.
Discover how Rigma turns pentesting into dynamic, measurable monitoring.
Discover how Rigma turns pentesting into dynamic, measurable monitoring.
After a traditional pentest
Forgotten PDF report
Forgotten PDF report
Forgotten PDF report
No proof of remediation
No proof of remediation
No proof of remediation
Costly retesting with no follow-up
Costly retesting with no follow-up
Costly retesting with no follow-up
Results scattered across providers
Results scattered across providers
Results scattered across providers
No executive-level metrics
No executive-level metrics
No executive-level metrics
With Rigma
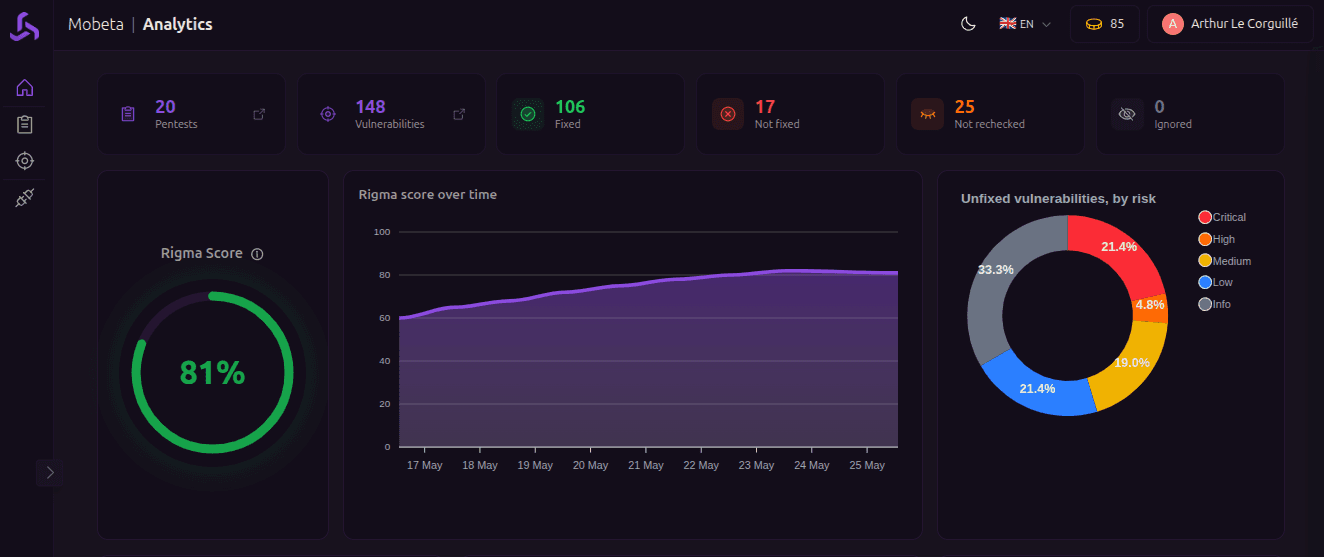
Real-time intuitive dashboard
Real-time intuitive dashboard
Real-time intuitive dashboard
One-click retest
One-click retest
One-click retest
Continuous monitoring, unlimited retests
Continuous monitoring, unlimited retests
Continuous monitoring, unlimited retests
Centralized and standardized results
Centralized and standardized results
Centralized and standardized results
COMEX-ready KPIs
COMEX-ready KPIs
COMEX-ready KPIs
Turn your pentest report into an interactive dashboard.
Book your 15-min demo
Book your 15-min demo
No commitment
·
Personalized by an expert
solution
3 simple steps to turn your pentests into continuous monitoring
3 simple steps to turn your pentests into continuous monitoring
From data import to compliance, every step saves you time and visibility.
Compatible with all your pentests.
step 1
.CSV
.PDF
.RIG
.CSV
.PDF
.RIG
Import your existing pentests into Rigma
Your pentests are automatically integrated into the platform (PDF, CSV, etc.) and your vulnerabilities are centralized.
Mobeta client ? No import needed. Your pentests are automatically integrated.
100% pentest traceability
WATCH VIDEO
Mobeta client ?
step 2
Vulnerability #
2
Not fixed
Vulnerability #
17
Not fixed
Vulnerability #
5
Not fixed
Vulnerability #
13
Not fixed
Vulnerability #
8
Not fixed
Vulnerability #
9
Not fixed
Re-verify your vulnerabilities continuously
A script runs automatically to confirm the remediation status. No human intervention required.
*Compared to the cost of a manual retest
~€1,000 saved per rechecked audit
WATCH VIDEO
step 3
10%
10%
Track your remediation in real time
Visualize your KPIs instantly and generate compliance certificates aligned with industry standards, ready for your COMEX.
+30% vulnerabilities fixed on average
WATCH VIDEO
50% of vulnerabilities remain unfixed after a manual retest
Book your demo with an expert
15 minutes
·
No commitment
pricing
The simple, cost-effective way to unlock the full value of your pentests
The simple, cost-effective way to unlock the full value of your pentests
Profitable from the very first pentest, Rigma reduces your retesting costs and simplifies vulnerability management with clear, flexible pricing.
Profitable from the very first pentest, Rigma reduces your retesting costs and simplifies vulnerability management
Profitable from the very first pentest, Rigma reduces your retesting costs and simplifies vulnerability management with clear, flexible pricing.
SaaS
On-Premise
On-premise : retest available on your internal systems.
Free
Try the platform for free.
0€
14-day trial period
Try Rigma
3 pentests included
Standard support
1 Rigma credit included
On-demand automated retests
Standard
For small teams getting started.
100€/month
Billed annually, cancel anytime
Try Rigma
3 pentests included
Standard support
1 Rigma credit included
On-demand automated retests
Pro
For growing security teams.
200€/month
Billed annually, cancel anytime
Try Rigma
Unlimited pentests
Priority support
1 Rigma credit included
On demand + weekly automated retests
2 workspaces
Enterprise
For large enterprises.
Custom
Custom quote, tailored to your needs
Try Rigma
SaaS
On-Premise
On-premise : retest available on your internal systems.
Free
Try the platform for free.
0€
14-day trial period
Try Rigma
3 pentests included
Standard support
1 Rigma credit included
On-demand automated retests
Standard
For small teams getting started.
100€/month
Billed annually, cancel anytime
Try Rigma
3 pentests included
Standard support
1 Rigma credit included
On-demand automated retests
Pro
For growing security teams.
200€/month
Billed annually, cancel anytime
Try Rigma
Unlimited pentests
Priority support
1 Rigma credit included
On demand + weekly automated retests
2 workspaces
Enterprise
For large enterprises.
Custom
Custom quote, tailored to your needs
Try Rigma
SaaS
On-Premise
On-premise : retest available on your internal systems.
Free
Try the platform for free.
0€
14-day trial period
Try Rigma
3 pentests included
Standard support
1 Rigma credit included
On-demand automated retests
Standard
For small teams getting started.
100€/month
Billed annually, cancel anytime
Try Rigma
3 pentests included
Standard support
1 Rigma credit included
On-demand automated retests
Pro
For growing security teams.
200€/month
Billed annually, cancel anytime
Try Rigma
Unlimited pentests
Priority support
1 Rigma credit included
On demand + weekly automated retests
2 workspaces
Enterprise
For large enterprises.
Custom
Custom quote, tailored to your needs
Try Rigma
Rigma Credits: how does it work?
1 credit = 100€
→ One credit automates the retest of a single vulnerability.
→ An automated vulnerability can be retested anytime, with no limits.
→ Credits are free for pentests performed by Mobeta.
faq
Everything you need to know before booking your demo
Everything you need to know before booking your demo
Compatibility, security, deployment… here are the answers to all your questions.
Is Rigma compatible with my existing pentests?
Yes. You can import your audit reports, whether they come from Mobeta or another provider. Rigma centralizes all your vulnerabilities in a single interface and enables automatic retest.
How many pentests does it take to make the solution worth it?
Rigma pays for itself from the very first pentest. Each avoided retest saves up to 1,000€ per restested audit, while speeding up your remediation timelines.
Does Rigma replace my internal ticketing solution?
No, Rigma complements it. Where a ticketing system manages tasks, Rigma technically verifies vulnerability remediation and provides actionable KPIs for the COMEX.
Is my data hosted in France?
Yes. All data is stored and processed on servers located in France, in compliance with GDPR and ISO 27001 standards. Our AI models are open source and hosted on Scaleway (SecNumCloud qualification in progress), ensuring full data sovereignty.
Can Rigma recheck vulnerabilities on my internal network?
Yes. The on-premise version of Rigma enables automatic re-verification of vulnerabilities on your internal systems, including Active Directory environments. It offers the same features as the SaaS version.
Can I try the platform before committing?
Yes. A free 14-day plan is available. It allows you to import 3 pentests and test the automatic re-verification feature.
How long does it take to deploy Rigma?
For the SaaS version, onboarding is instant. For the on-premise version, installation is very simple: 2 Docker commands, 5 minutes, and the solution is up and running.
How does the demo work?
A personalized 15-minute session with a Rigma expert. You'll see the platform live and can ask all your questions, no commitment required.
Is Rigma compatible with my existing pentests?
Yes. You can import your audit reports, whether they come from Mobeta or another provider. Rigma centralizes all your vulnerabilities in a single interface and enables automatic retest.
How many pentests does it take to make the solution worth it?
Rigma pays for itself from the very first pentest. Each avoided retest saves up to 1,000€ per restested audit, while speeding up your remediation timelines.
Does Rigma replace my internal ticketing solution?
No, Rigma complements it. Where a ticketing system manages tasks, Rigma technically verifies vulnerability remediation and provides actionable KPIs for the COMEX.
Is my data hosted in France?
Yes. All data is stored and processed on servers located in France, in compliance with GDPR and ISO 27001 standards. Our AI models are open source and hosted on Scaleway (SecNumCloud qualification in progress), ensuring full data sovereignty.
Can Rigma recheck vulnerabilities on my internal network?
Yes. The on-premise version of Rigma enables automatic re-verification of vulnerabilities on your internal systems, including Active Directory environments. It offers the same features as the SaaS version.
Can I try the platform before committing?
Yes. A free 14-day plan is available. It allows you to import 3 pentests and test the automatic re-verification feature.
How long does it take to deploy Rigma?
For the SaaS version, onboarding is instant. For the on-premise version, installation is very simple: 2 Docker commands, 5 minutes, and the solution is up and running.
How does the demo work?
A personalized 15-minute session with a Rigma expert. You'll see the platform live and can ask all your questions, no commitment required.
Is Rigma compatible with my existing pentests?
Yes. You can import your audit reports, whether they come from Mobeta or another provider. Rigma centralizes all your vulnerabilities in a single interface and enables automatic retest.
How many pentests does it take to make the solution worth it?
Rigma pays for itself from the very first pentest. Each avoided retest saves up to 1,000€ per restested audit, while speeding up your remediation timelines.
Does Rigma replace my internal ticketing solution?
No, Rigma complements it. Where a ticketing system manages tasks, Rigma technically verifies vulnerability remediation and provides actionable KPIs for the COMEX.
Is my data hosted in France?
Yes. All data is stored and processed on servers located in France, in compliance with GDPR and ISO 27001 standards. Our AI models are open source and hosted on Scaleway (SecNumCloud qualification in progress), ensuring full data sovereignty.
Can Rigma recheck vulnerabilities on my internal network?
Yes. The on-premise version of Rigma enables automatic re-verification of vulnerabilities on your internal systems, including Active Directory environments. It offers the same features as the SaaS version.
Can I try the platform before committing?
Yes. A free 14-day plan is available. It allows you to import 3 pentests and test the automatic re-verification feature.
How long does it take to deploy Rigma?
For the SaaS version, onboarding is instant. For the on-premise version, installation is very simple: 2 Docker commands, 5 minutes, and the solution is up and running.
How does the demo work?
A personalized 15-minute session with a Rigma expert. You'll see the platform live and can ask all your questions, no commitment required.

Discover how Rigma unlocks the full value of your pentests
Discover how Rigma unlocks the full value of your pentests
In 15 minutes, learn how to automate your retests and track your security progress in real time.
Book your 15-min demo
No commitment
·
Personalized by an expert
partners & compliance
A secure, certified solution built for the most demanding environments
Secure and certified for the most demanding environments.
Compliant with NIS2, DORA, and ISO 27001 standards, and supported by leading cybersecurity players.
Already used by over 20 companies, including…
Already used by over 20 companies, including…
"Simple and fast setup. The dashboard gives a clear view of vulnerabilities and remediation progress. It's a straightforward, effective tool, a real step up from PDF reports."
Sidiki Mariko
DevOps/Sys/SecOps
DevOps/Sys/SecOps
"Rigma was a huge plus for our teams, who were able to validate their remediation work independently. It significantly accelerated our vulnerability remediation."
Joffrey Mazier
Head of Customer Success
Head of Customer Success
"Simple and fast setup. The dashboard gives a clear view of vulnerabilities and remediation progress. It's a straightforward, effective tool, a real step up from PDF reports."
Sidiki Mariko
DevOps/Sys/SecOps
"Rigma was a huge plus for our teams, who were able to validate their remediation work independently. It significantly accelerated our vulnerability remediation."
Joffrey Mazier
Head of Customer Success
Rigma meets the highest industry standards.
Rigma meets the highest industry standards.
Certified auditors
A team of experts holding OSCP & OSWE certifications.
Certified auditors
A team of experts holding OSCP & OSWE certifications.
Regulatory compliance
Fully compliant with NIS2, DORA, and HDS standards.
Regulatory compliance
Fully compliant with NIS2, DORA, and HDS standards.
Sovereign Hosting
Hosted on Scaleway, including open-source AI models.
Sovereign Hosting
Hosted on Scaleway, including open-source AI models.
Recognized partners
Supported by Bpifrance and "CCI Paris Île-de-France", ensuring reliability and innovation.
Recognized partners
Supported by Bpifrance and "CCI Paris Île-de-France", ensuring reliability and innovation.