
step 1
Import your existing pentests into Rigma
Your pentests are automatically integrated into the platform (PDF, CSV, etc.) and your vulnerabilities are centralized.
100% pentest traceability
Pentest experts for over 10 years
Centralize, recheck, and track your vulnerabilities continuously.



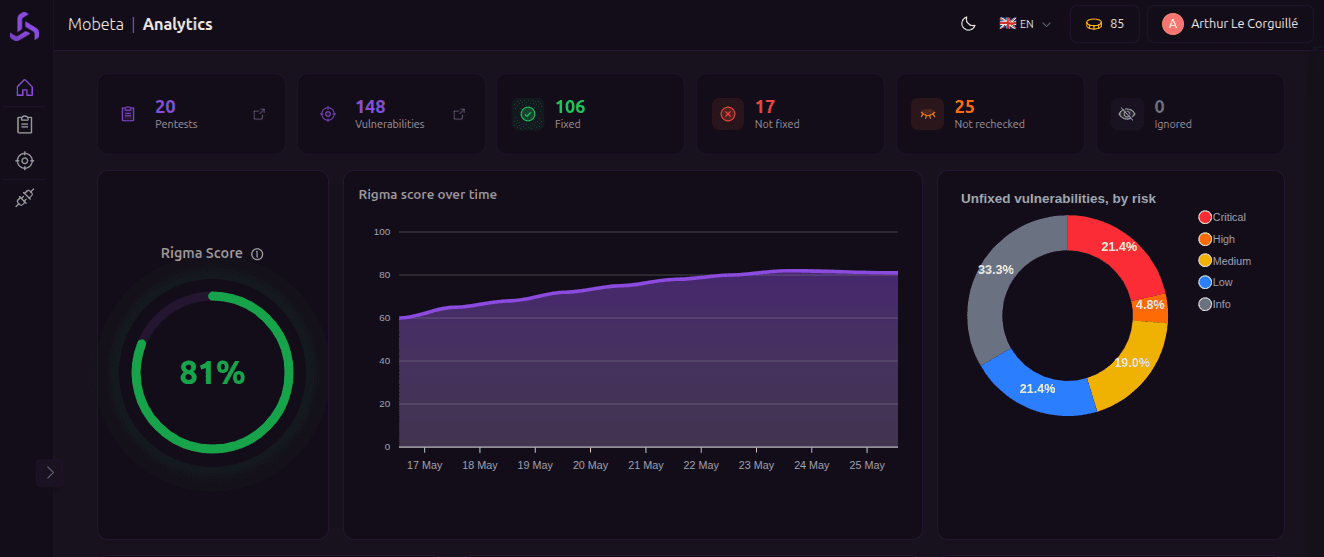
Discover how Rigma turns pentesting into dynamic, measurable monitoring.
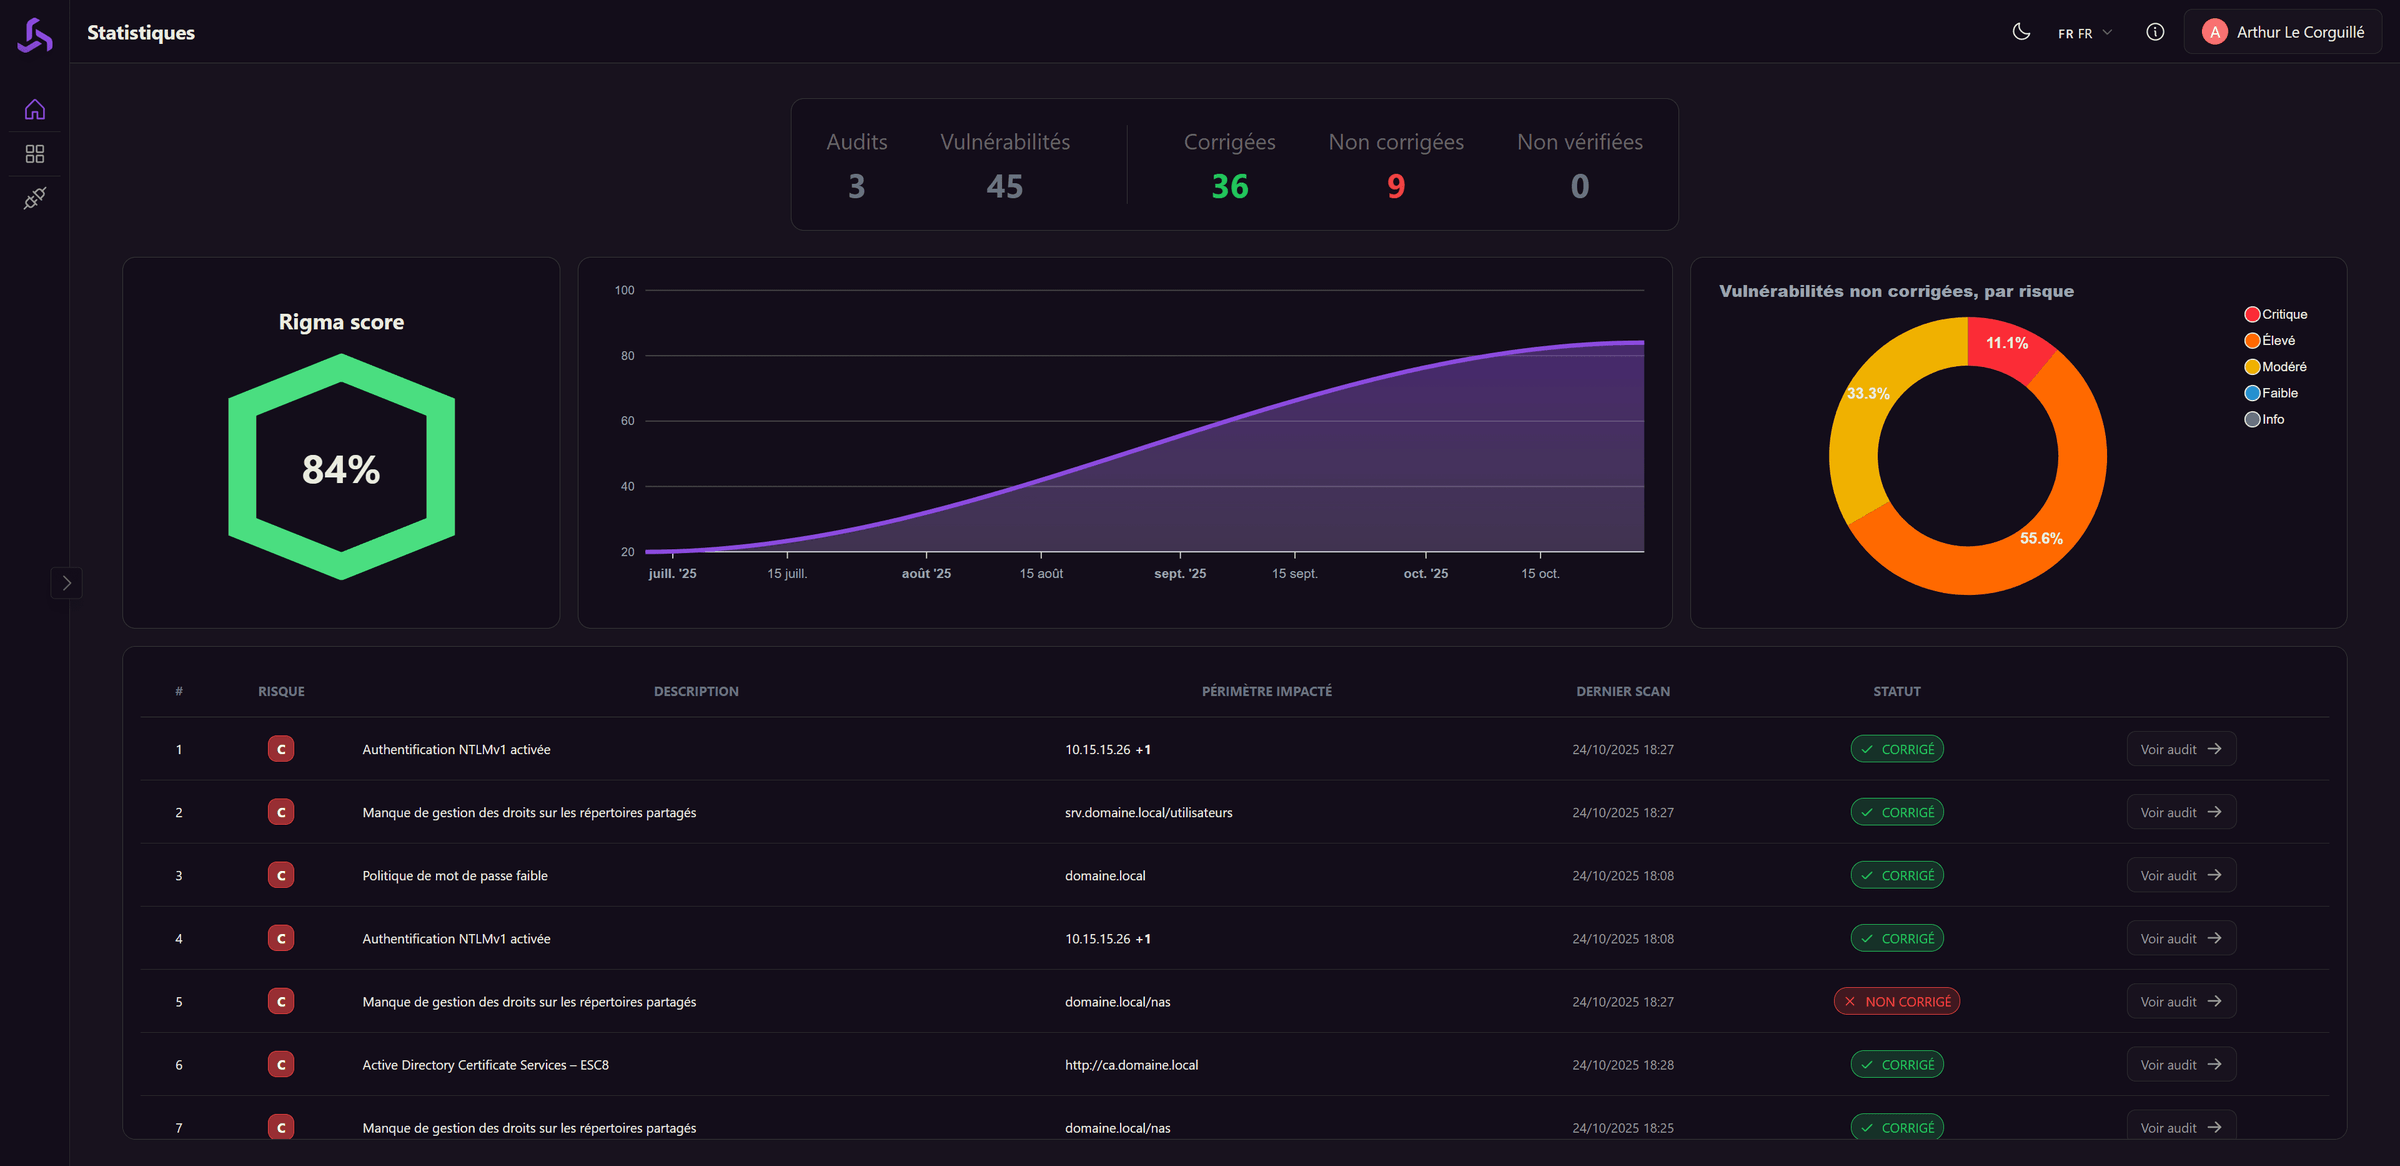
Turn your pentest report into an interactive dashboard.
From data import to compliance, every step saves you time and visibility.
Compatible with all your pentests.
step 1
Your pentests are automatically integrated into the platform (PDF, CSV, etc.) and your vulnerabilities are centralized.
100% pentest traceability
step 2
A script runs automatically to confirm the remediation status. No human intervention required.
step 3
Visualize your KPIs instantly and generate compliance certificates aligned with industry standards, ready for your COMEX.
+30% vulnerabilities fixed on average
50% of vulnerabilities remain unfixed after a manual retest
No import needed. Your pentests are automatically integrated.
Compared to the cost of a manual retest
Try the platform for free.
0€
14-day trial period
For small teams getting started.
100€/month
Billed annually, cancel anytime
For growing security teams.
200€/month300€/month
Billed annually, cancel anytime
For large enterprises.
Custom
Custom quote, tailored to your needs
1 credit = 100€
→ One credit automates the retest of a single vulnerability.
→ An automated vulnerability can be retested anytime, with no limits.
→ Credits are free for pentests performed by Mobeta.
Compatibility, security, deployment… here are the answers to all your questions.
Yes. You can import your audit reports, whether they come from Mobeta or another provider. Rigma centralizes all your vulnerabilities in a single interface and enables automatic retest.
Rigma pays for itself from the very first pentest. Each avoided retest saves up to 1,000€ per retested audit, while speeding up your remediation timelines.
No, Rigma complements it. Where a ticketing system manages tasks, Rigma technically verifies vulnerability remediation and provides actionable KPIs for the COMEX.
Yes. All data is stored and processed on servers located in France, in compliance with GDPR and ISO 27001 standards. Our AI models are open source and hosted on Scaleway (SecNumCloud qualification in progress), ensuring full data sovereignty.
Yes. The on-premise version of Rigma enables automatic re-verification of vulnerabilities on your internal systems, including Active Directory environments. It offers the same features as the SaaS version.
Yes. A free 14-day plan is available. It allows you to import 3 pentests and test the automatic re-verification feature.
For the SaaS version, onboarding is instant. For the on-premise version, installation is very simple: 2 Docker commands, 5 minutes, and the solution is up and running.
A personalized 15-minute session with a Rigma expert. You'll see the platform live and can ask all your questions, no commitment required.
In 15 minutes, learn how to automate your retests and track your security progress in real time.
A secure, certified solution built for the most demanding environments Secure and certified for the most demanding environments.
Compliant with NIS2, DORA, and ISO 27001 standards, and supported by leading cybersecurity players.
Already used by over 20 companies, including…
Sidiki Mariko
DevOps/Sys/SecOps
Joffrey Mazier
Head of Customer Success
Sidiki Mariko
DevOps/Sys/SecOps
Joffrey Mazier
Head of Customer Success
Rigma meets the highest industry standards.
Certified auditors
A team of experts holding OSCP & OSWE certifications.
Regulatory compliance
Fully compliant with NIS2, DORA, and HDS standards.
Sovereign Hosting
Hosted on Scaleway, including open-source AI models.
Recognized partners
Supported by Bpifrance and "CCI Paris Île-de-France", ensuring reliability and innovation.